Anthropic's Frontier Red Team proved that discovering and patching individual vulnerabilities scales poorly against AI-equipped adversaries. By executing an automated three-pass methodology powered by Claude across 25 major open source repositories, the model uncovered 493 attack surface flaws. The most critical case occurred in OpenSSH, where roughly 4,500 lines of experimental post-quantum cryptography code were reachable by unauthenticated clients in default configurations, accounting for 16 percent of the sshd daemon's pre-authentication codebase.
1. The vulnerability patching fallacy: why the reactive CVE paradigm is broken
For decades, software defense has adhered to a predictable and increasingly unsustainable lifecycle: a security vulnerability is identified, assigned a CVE number, maintainers rush to develop a patch, and system administrators update production servers. Yet this reactive model suffers from a fatal architectural flaw: fixing a critical remote code execution vulnerability provides zero visibility into how many other latent bugs remain untouched within the same codebase.
As frontier artificial intelligence models acquire sophisticated code comprehension and automated exploit generation capabilities, the asymmetric advantage shifts heavily toward attackers. When adversaries can programmatically scan millions of lines of source code to discover memory safety flaws or protocol edge cases, defensive postures that rely solely on reactive bug disclosures become obsolete.
In response to this structural challenge, Anthropic's Frontier Red Team, led by security researcher Chris Rohlf, introduced a fundamental defensive framework: Attack Surface Reduction (ASR). Rather than attempting to find every individual software bug, ASR uses artificial intelligence to systematically map reachable code paths and restrict access to non-essential functionality, relocating complex routines behind authentication gates, enforcing explicit opt-in flags, or postponing parsing deeper into protocol state transitions.
2. The massive audit: 25 open source repositories and 493 architectural flaws
To evaluate whether frontier artificial intelligence could reliably automate attack surface analysis across diverse architectures, Anthropic deployed Claude across 25 established open source projects representing over 5 million lines of code written in C, C++, Java, PHP, and Python. Claude generated an exhaustive inventory of over 17,000 configuration options, identifying 3,842 settings directly relevant to security controls.
The target projects were divided into three operational categories:
Public projects (10 repositories): built to process input from arbitrary, untrusted clients, such as recursive DNS resolvers or edge proxy caches.
Gated projects (11 repositories): designed to serve authenticated clients presenting valid credentials, cryptographic keys, or certificates. While listening on public network sockets, no substantive application logic should be reachable prior to authentication.
Private projects (4 repositories): tools deployed within perimeter-protected environments where access controls are largely handled externally.
The findings were eye-opening: Claude uncovered 493 distinct attack surface issues. In every single one of the 11 Gated projects, code was unintentionally reachable prior to authentication. Specifically, Claude identified 93 unnecessary pre-authentication surfaces enabled by default, 37 execution points where state was committed before authentication verification, and 61 configuration combinations that silently disabled or weakened access controls.
3. Case study OpenSSH: when the world's most audited codebase exposes critical attack surface
OpenSSH is the foundational transport layer powering remote administration across billions of Linux servers, enterprise cloud instances, and critical telecommunications infrastructure. Because of its mission-critical ubiquity, OpenSSH's C codebase is widely recognized as one of the most thoroughly audited and hardened software projects in existence.
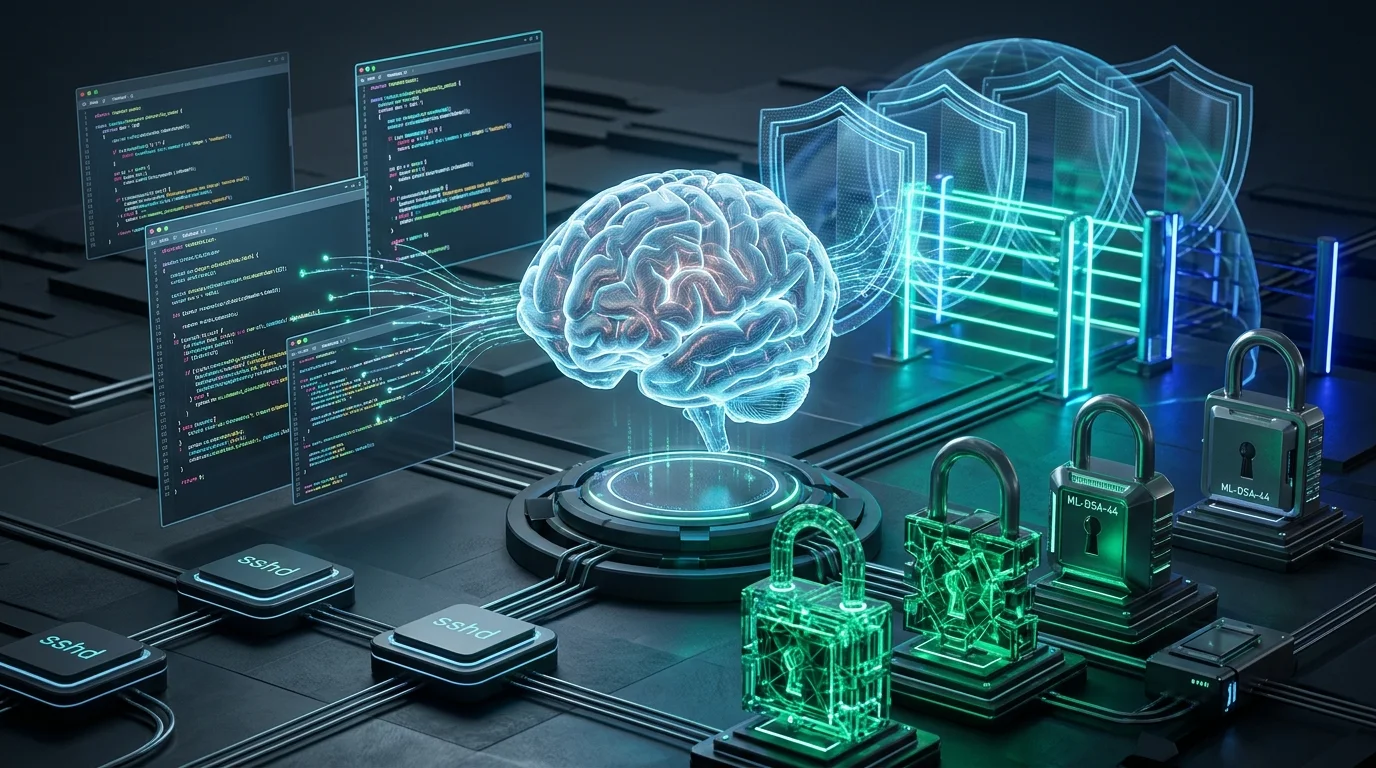
Yet, when Claude traced input paths within the sshd daemon in the 10.4 release, it discovered an astonishing architectural vulnerability: approximately 4,500 lines of complex, newly added experimental code for the ML-DSA-44 post-quantum signature algorithm were reachable by unauthenticated remote clients under standard default configurations.
ML-DSA was not enabled by default, but the execution path was reachable regardless, even when administrators explicitly configured policies excluding the algorithm. The daemon parsed whichever key blob the remote client supplied and, for certificates, performed complete public key signature verifications before verifying whether the key algorithm was allowed. Those 4,500 lines of post-quantum C code accounted for approximately 16 percent of OpenSSH's entire pre-authentication attack surface in default builds.
/*
 * OpenSSH Execution Path Comparison: 10.4 vs 10.5 vs 10.6
 * Conceptual demonstration of pre-authentication bypass and final parser gating
 */

// VULNERABILITY IN OPENSSH 10.4:
// sshd deserializes keys and verifies signatures before consulting configuration policy
int process_client_key_v10_4(struct ssh *ssh, struct sshkey *key) {
    // 1. Parses unverified raw key blob sent by unauthenticated client
    parse_raw_postquantum_key_blob(key->blob); // ~4,500 lines of complex C reachable

    // 2. Verifies embedded Certificate Authority (CA) signature
    verify_ca_signature(key->cert, key->ca_pubkey);

    // 3. ONLY THEN checks if the algorithm is permitted in sshd_config
    if (!is_algorithm_allowed(key->algorithm)) {
        return SSH_ERR_KEY_TYPE_UNKNOWN; // Adversary already exercised C memory parser
    }
    return 0;
}

// DEFINITIVE FIX IN OPENSSH 10.6:
// Allowlist verification executed directly inside low-level parser before memory allocation
int process_client_key_v10_6(struct ssh *ssh, const u_char *blob, size_t blen) {
    int alg_id = peek_key_algorithm_header(blob, blen);

    // Hard gate: if algorithm is not explicitly allowed in configuration,
    // immediately discard packet without executing cryptographic routines
    if (!is_algorithm_in_allowlist(ssh->config, alg_id)) {
        ssh_log("Connection attempt with unauthorized algorithm rejected pre-parse");
        return SSH_ERR_ACCESS_DENIED;
    }

    return safe_deserialize_and_verify(blob, blen);
}
4. The patch iteration: how Claude caught two subtle bypasses in OpenSSH 10.5
Anthropic responsibly reported these findings alongside proposed patches to OpenSSH maintainers. The resulting OpenSSH 10.5 release relocated the algorithm policy verification ahead of key parsing. However, when Anthropic re-ran Claude against the updated 10.5 codebase, the AI identified two sophisticated bypass conditions that had escaped human review:
First bypass: algorithm advertisement mismatch. The 10.5 check validated the algorithm name advertised during initial protocol negotiation, but the low-level C parser selected its deserialization routine based on an internal type string embedded inside the payload. An attacker could advertise a benign ssh-ed25519 key to satisfy policy checks, while transmitting an ML-DSA payload that forced sshd into experimental parsing routines.
Second bypass: Certificate Authority signature evaluation. Certificate key types were enabled by default. If an unauthenticated attacker supplied an arbitrary certificate, sshd deserialized the embedded CA public key and executed a full signature verification routine before evaluating server policy. This left every signature verification routine in the compiled binary exposed to any client capable of establishing a TCP handshake.
Working in close collaboration with OpenSSH maintainers, Anthropic developed a proof of concept that led to the definitive patches shipped in OpenSSH 10.6. The final solution placed policy checks directly inside the parsing engine itself. The encoded key type and CA signature algorithm are verified against allowlists prior to deserialization, permanently eliminating roughly 20 percent of reachable pre-authentication code in standard OpenSSH deployments.
5. Architectural patterns in other projects: fail-open DNS rules and 21-year-old bugs
OpenSSH was not an isolated outlier. Across the remaining 24 audited projects, Claude surfaced recurring systemic vulnerabilities caused by complex configuration interactions:
Hostname deny lists failing open: in four unrelated projects, Claude detected an identical architectural flaw. When administrators wrote access rules using hostnames or wildcards rather than static IP addresses, the server compared client connections against that rule. However, if reverse DNS lookups were disabled for performance (as is standard in high throughput services), the server only possessed the numerical IP string. Because a hostname pattern never matches a numeric IP, the deny rule never triggered, causing access controls to fail open and grant unauthorized access.
Conflicting options dropping certificate requirements: in another enterprise networking project, an administrator could configure mandatory TLS client certificates. A separate configuration flag was intended to delay verification until required; in practice, combining these settings completely disabled certificate enforcement without logging warnings. That conflicting behavior had existed undetected for 21 years.
| Audit Metric / Category | Public Projects | Gated Projects (Authenticated) | Private Projects | Overall Total |
|---|---|---|---|---|
| Audited repositories | 10 projects | 11 projects | 4 projects | 25 projects (>5M lines of code) |
| Configuration options analyzed | 7,420 options | 6,890 options | 2,690 options | 17,000 options (3,842 security-critical) |
| Attack surface issues discovered | 178 findings | 224 findings (highest severity) | 91 findings | 493 total issues surfaced |
| Unnecessary pre-authentication code | N/A (Public access) | 93 pre-auth surfaces identified | 12 exposed paths | 105 pre-auth surfaces mitigated |
| Pre-auth reduction in OpenSSH | N/A | ~20% pre-auth code eliminated | N/A | ~4,500 lines of post-quantum C gated |
6. The three-pass methodology: integrating AI attack surface reduction into CI/CD
Anthropic structured these defensive techniques into an automated skill being integrated into OSS-Scanner. The workflow operates across three distinct passes with pristine context isolation:
Pass 1 (Default configuration): identifies code reachable in default builds that serves no legitimate default functionality.
Pass 2 (Early reachability): maps routines executing prior to authentication boundaries, cryptographic handshakes, or protocol transitions.
Pass 3 (Configuration interactions): surfaces conflicting options that silently disable protections or create undefined execution states.
Crucially, Claude validates candidate patches by executing unit test suites, regression test frameworks, and dynamic traces, ensuring that default application behavior remains untouched while attack surfaces shrink.
7. Conclusion: why proactive reachability analysis is cybersecurity's new frontier
The OpenSSH audit demonstrates an inescapable reality: if software subjected to twenty-five years of world-class cryptanalytic scrutiny inadvertently exposed 16 percent of its pre-authentication attack surface, virtually every modern corporate codebase harbors severe reachability flaws.
The most impactful role for artificial intelligence in software engineering is not merely generating boilerplate code, but acting as an automated, tireless security architect embedded directly within continuous integration pipelines. By systematically shrinking reachable code, organizations protect their infrastructure not just against known CVEs, but against zero-day exploits before they are ever authored.